Investigating Suspicious Windows Processes
A practical investigation workflow using Windows logs, Sysmon, Process Explorer and Autoruns.
Technical write-ups from my labs: what I built, what broke and what I learned. Each one was first published on Medium.
Saved articles stay in this browser. No account needed.
A practical investigation workflow using Windows logs, Sysmon, Process Explorer and Autoruns.
Authorization, integrity checks, sandboxing, and the limits of a Windows AI assistant.
An attack-chain walkthrough in my own lab, with event sources and defensive analysis.
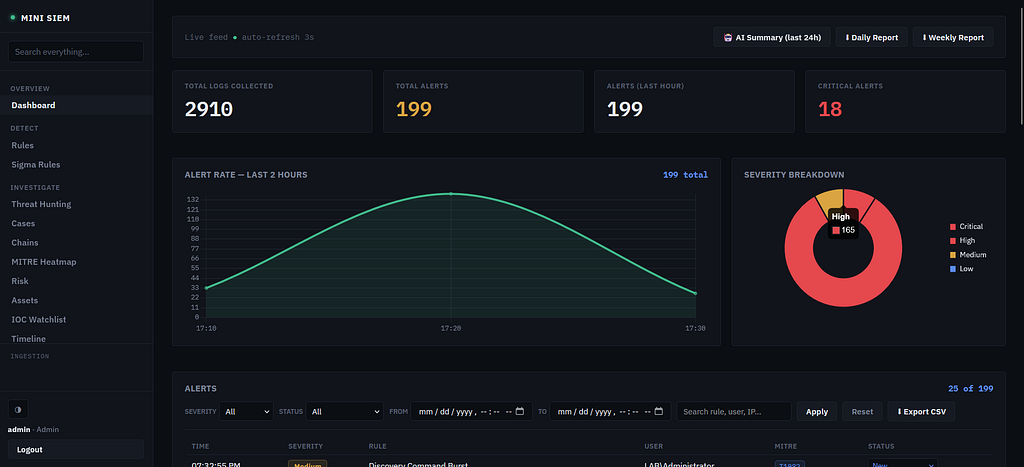
Ten Atomic Red Team tests and a parser bug that prevented a detection rule from firing.
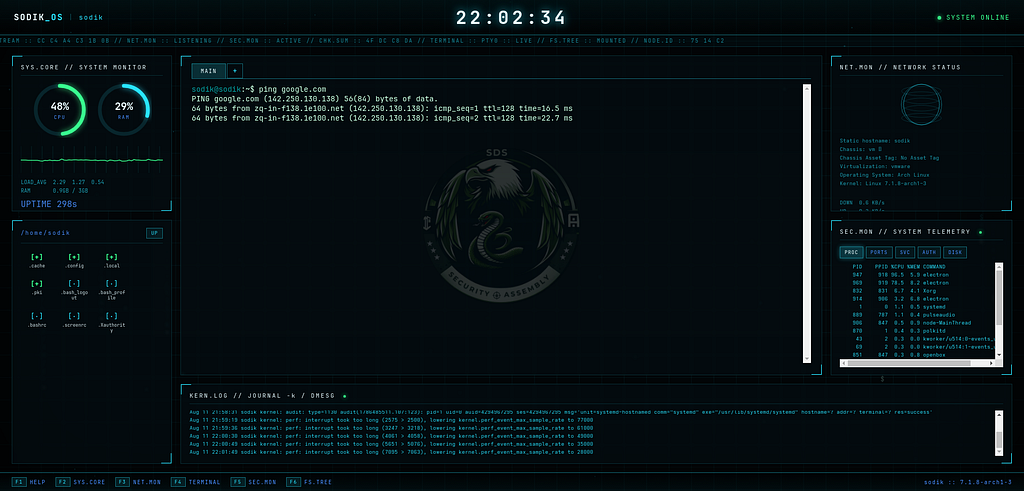
A bootable Arch-based image with a custom interface, terminal, and system telemetry.
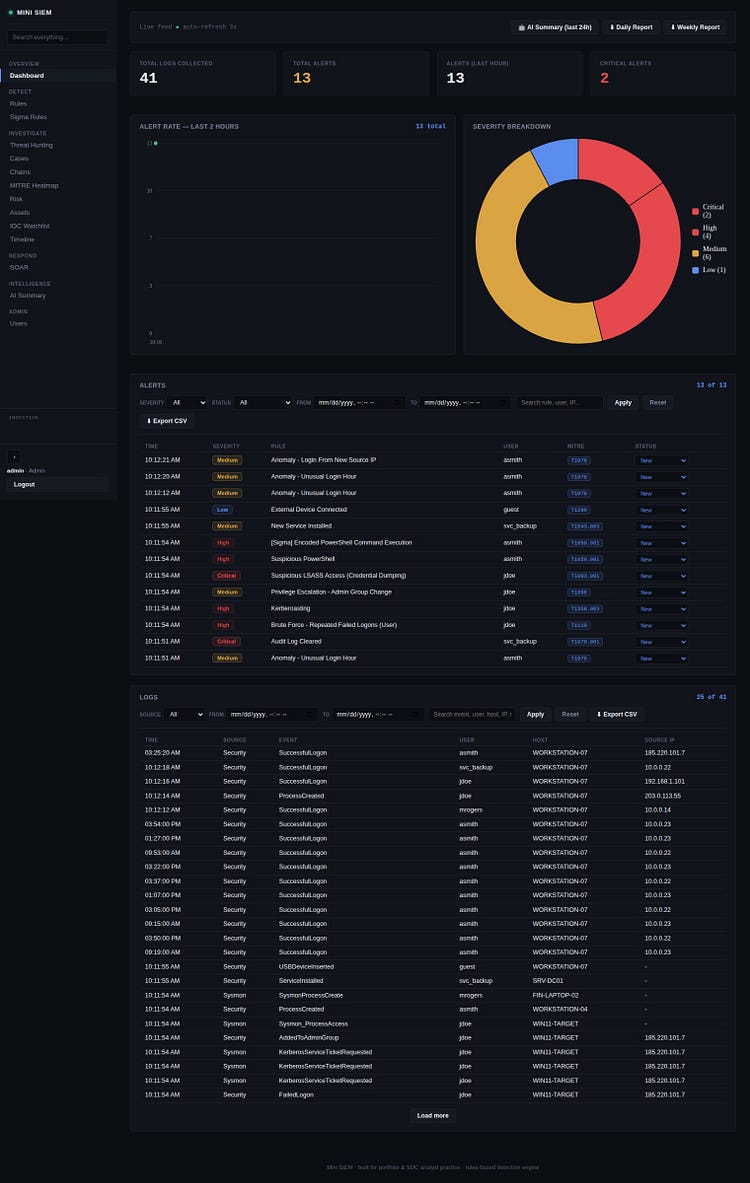
Log ingestion, detection rules, and the problems I found while testing the pipeline.
Try another topic or a broader search.