<style>#root [style*="opacity:0"] { opacity: 1 !important; transform: none !important; }</style>

Detection Engineering

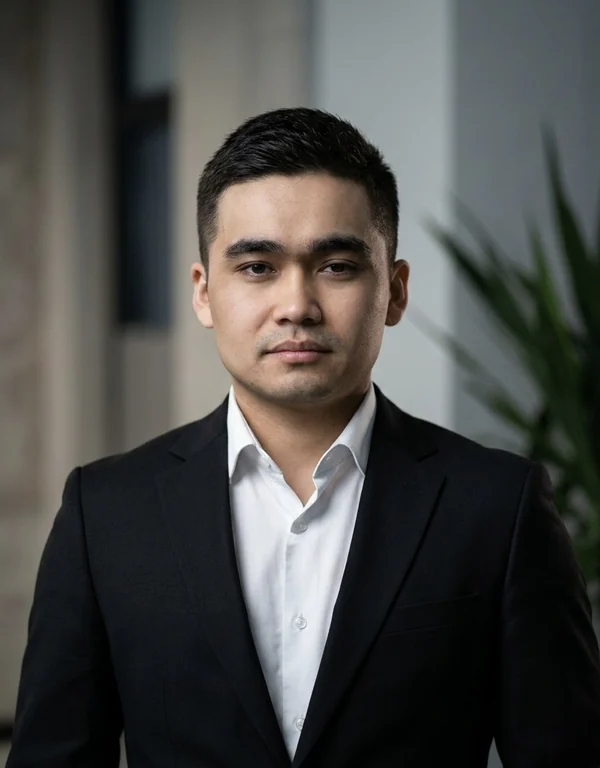
Portrait of Sodik Tursunboev
Holder
Sodik Tursunboev
Role
Cybersecurity Analyst | Detection Engineer
Based in
Warsaw, Poland
CEH credential ID
ECC5142870936

Sodik Tursunboev

Proactive threat hunting and robust detection, tested against real attacks in an enterprise-style lab.

I build defensive security systems, emulate real attacks, and turn the results into stronger detections.

Certified Ethical Hacker (CEH)Issued by EC-Council, October 2025Verify credential

Certifications

Select a certificate to view it full size.

Certification

Certified Ethical Hacker (CEH)

Issued by EC-Council, October 2025

Credential ID ECC5142870936

Verify credential
Official training

CEH v13 official training

Completed with EC-Council, July 2025

Credential ID 762648

Verify credential
Top 1%
TryHackMe, worldwide238 rooms and 49 badges across SOC, red team and penetration testing.View profile

Course certificates

Foundations of Cybersecurity

Google, on Coursera

November 2024

Verify credential

Play It Safe: Manage Security Risks

Google, on Coursera

November 2024

Verify credential

Connect and Protect: Networks and Network Security

Google, on Coursera

November 2024

Verify credential

Learn Ethical Hacking From Scratch

Zaid Sabih and zSecurity, on Udemy

November 2023, 16 hours

Verify credential
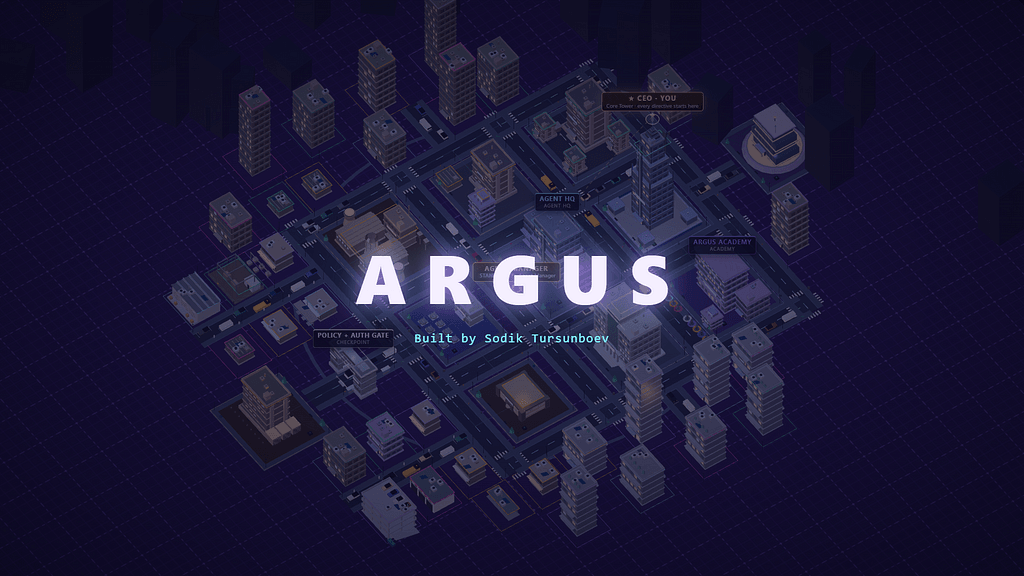
ARGUS AI City from above: an isometric city where every robot is an ARGUS agent

ARGUS City

ARGUS

Every robot is a real ARGUS agent. Every light is backend state.

Projects

Security engineering

ARGUS

A local AI assistant and Windows threat monitor where every action passes a fail-closed security gate.

Lines of code
63K+
Test suites
109
ATT&CK detectors
16

Detection engineering

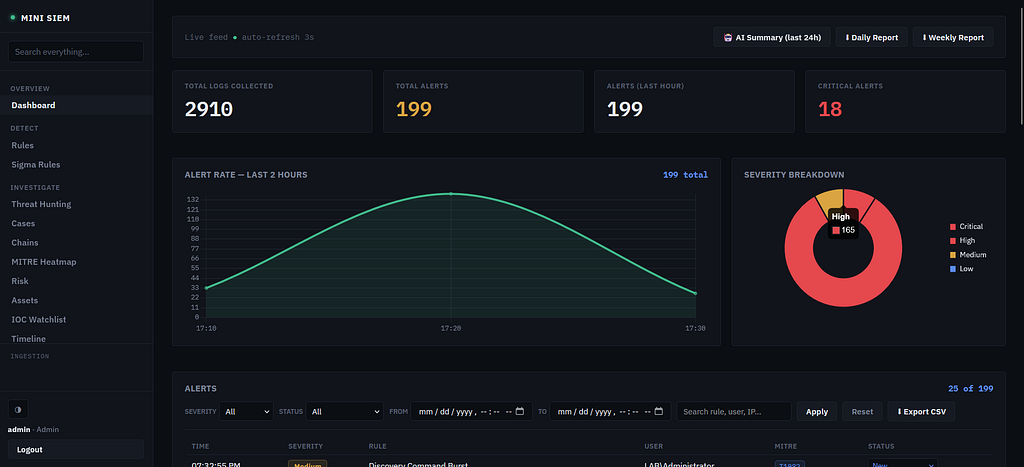
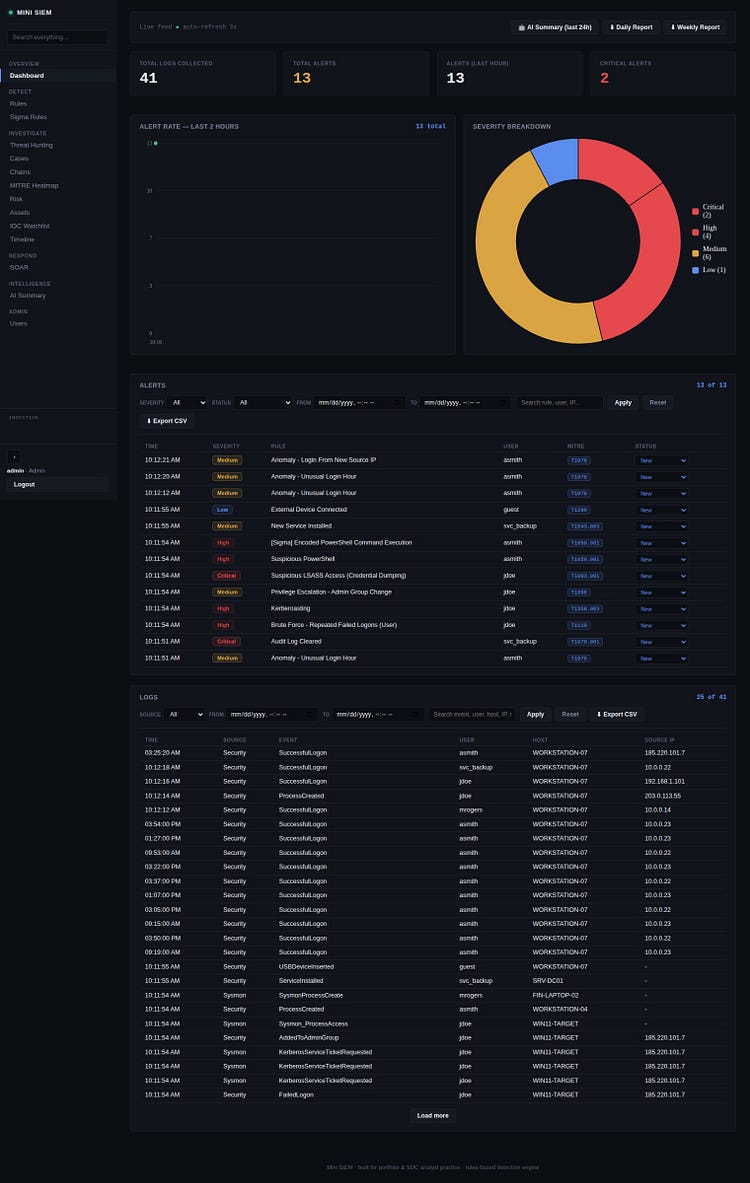
Custom SIEM + Sentinel BAS

A Python SIEM paired with an attack-simulation engine that measures whether each detection actually fires.

Detection rules
35
Measured coverage
70%
Correlation window
60 min

Operating system

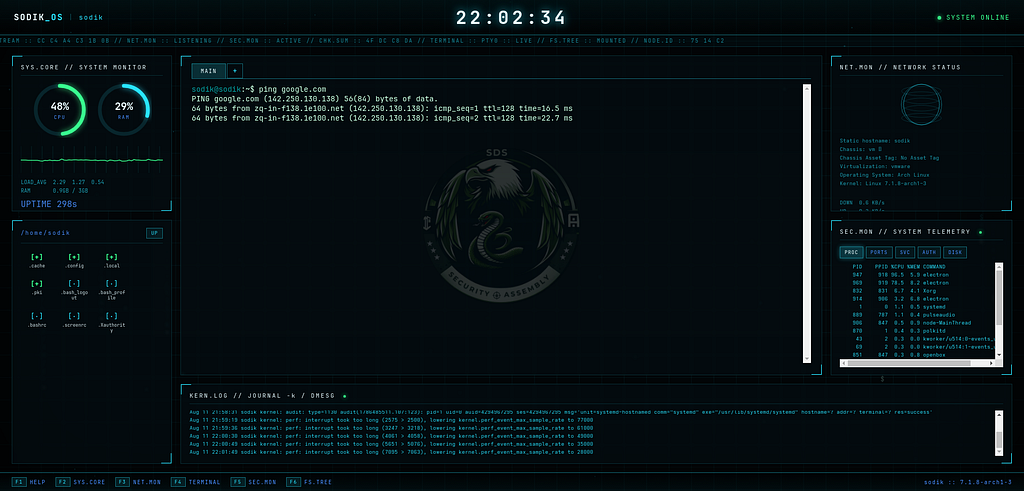
SODIK OS

A bootable Arch Linux distribution that starts straight into a cinematic hacker interface: a real root shell, live system telemetry and an AI voice that narrates the boot.

Built from scratch with archiso
Live ISO
The interface is the session
No desktop
CPU, RAM, processes, ports, auth logs
Real data

More projects

Purple team lab

Active Directory lab

An enterprise Active Directory lab for adversary emulation and SOC detection, mapping attack paths to Windows and Sysmon telemetry and MITRE ATT&CK.

  • Active Directory
  • Sysmon
  • MITRE ATT&CK

The attack chain, and the event that caught each stage

  1. 1–2LLMNR poisoning, then a WinRM shellDetected by: 46244769
  2. 3AS-REP Roasting a service accountDetected by: WinRM 914672
  3. 4A cached domain admin credential dumpedDetected by: 5379
  4. 5Domain accounts enumerated over LDAPDetected by: Sysmon 3
  5. 6A reused password: SSH into the domain controllerDetected by: OpenSSH 44624
  6. 7LSASS dumped with comsvcs.dllDetected by: Sysmon 1
  7. 8DCSync, then a Golden TicketDetected by: 4662
  8. 9The dump copied out over SCPDetected by: Sysmon 3

Detection lab

How I prove a detection works: attacks simulated against my own SIEM, and the Sigma rules that catch them.

Sentinel BAS ran ten Atomic Red Team tests on my lab host and matched each one to the alerts my SIEM raised, by ATT&CK technique, host and timing.

70%measured coverage

7 detected, 3 missed

  • ExecutionT1059.001PowerShellEncoded PowerShell commandDetectedin 0 s
  • PersistenceT1136.001Local accountCreate a new local userDetectedin 0 s
  • PersistenceT1547.001Registry Run keysRegistry Run key persistenceDetectedin 0 s
  • PersistenceT1543.003Windows serviceInstall a new serviceDetectedin 4 s
  • PersistenceT1053.005Scheduled taskCreate a scheduled taskMissedNo alert
  • Defense evasionT1070.001Clear Windows event logsClear the Security event logMissedNo alert
  • Credential accessT1003.001LSASS memoryDump LSASS memoryDetectedin 0 s
  • Credential accessT1558.003KerberoastingRequest SPN ticketsMissedNo alert
  • DiscoveryT1082System information discoveryDiscovery command burstDetectedin 21 s
  • ImpactT1490Inhibit system recoveryDelete volume shadow copiesDetectedin 0 s

A replay of the recorded run. Detected means a matching alert within 60 seconds; none was delayed.

The Kerberoasting miss exposed a rule that could never fire: it relied on TicketEncryptionType, which the pipeline never extracted.

Full results in the SIEM case study

Writing

Technical write-ups from my labs, published on Medium.

About

Cybersecurity professional specializing in detection engineering, offensive security, and security operations. CEH v13 certified, combining an attacker mindset with defensive engineering to emulate adversary techniques and build detections that improve visibility and incident response.

Hands-on experience spans Active Directory security, web exploitation, SIEM development, threat hunting, security automation, and AI systems engineering, translating attacker behavior into actionable detections using MITRE ATT&CK and Sigma.

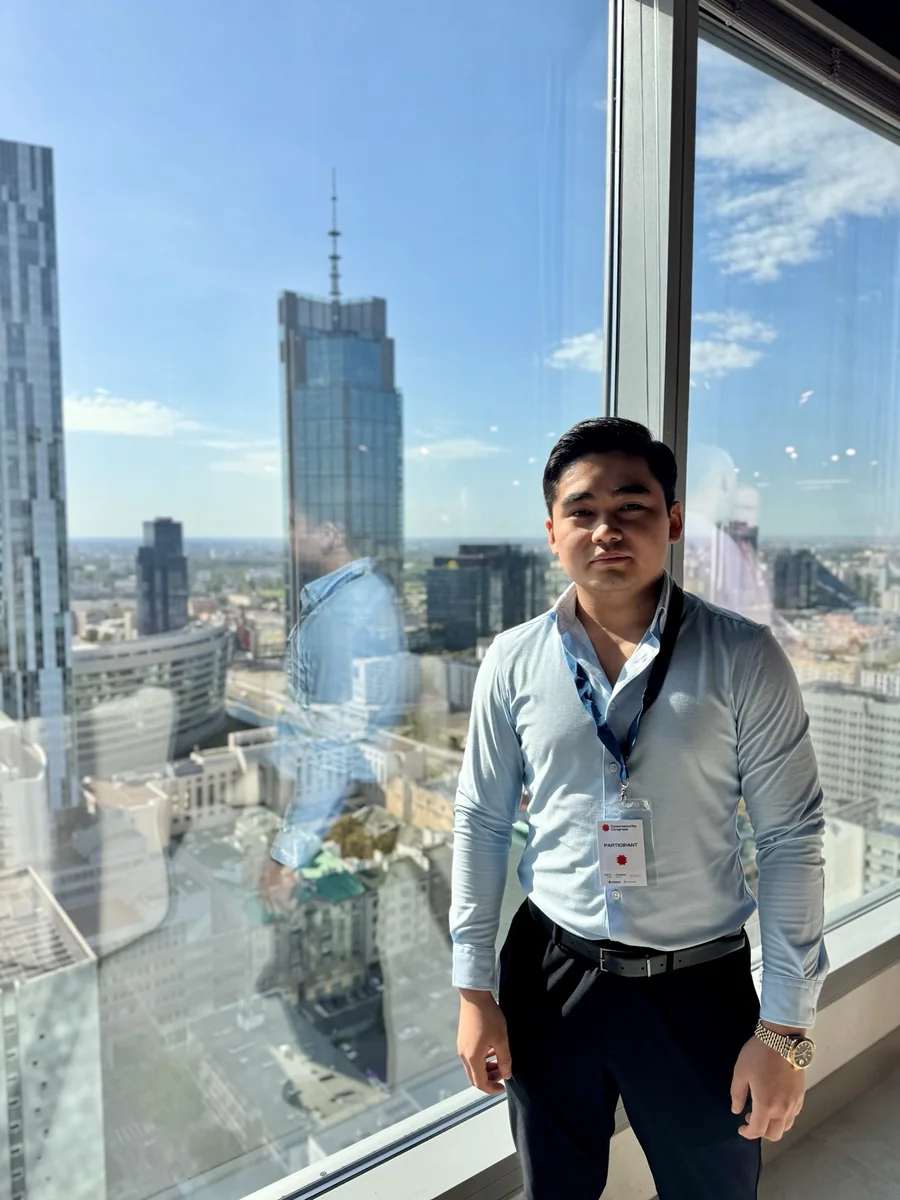
Sodik Tursunboev at a cybersecurity congress, with the Warsaw skyline behind him
At a cybersecurity congress in Warsaw

Technical focus

  • Purple team operations
  • Detection engineering
  • Breach and attack simulation
  • SIEM development
  • Threat hunting
  • Active Directory security
  • MITRE ATT&CK
  • Sigma rules
  • Security automation
  • AI agent systems
  • Local-first AI
  • Secure AI orchestration
  • Windows automation

DefendEmulateBuild

Contact and socials

Write to me about detection engineering, adversary simulation or security systems. Your message goes straight to my inbox.

Prefer email?

hello@sodik.eu
Save contact

Based in Warsaw, Poland